This is the written version of SwiftShop security lab, taken from the lesson itself. The simulations, drag-and-drop activities and quizzes only work in the interactive lesson.
TRAINING ENVIRONMENT — SwiftShop Security Lab — deliberately insecure — all data is fake — do not enter real credentials
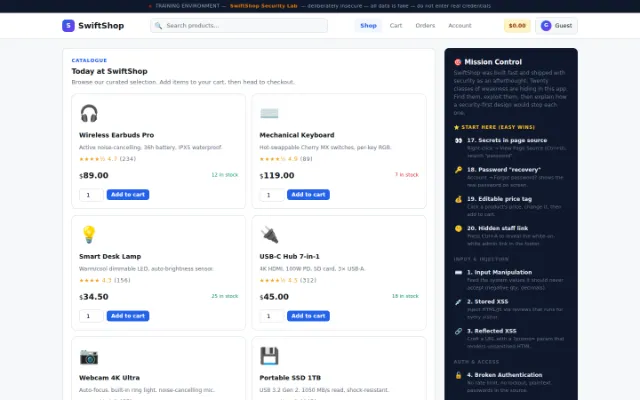
Today at SwiftShop
Browse our curated selection. Add items to your cart, then head to checkout.
Active noise-cancelling, 36h battery, IPX5 waterproof.
Hot-swappable Cherry MX switches, per-key RGB.
Warm/cool dimmable LED, auto-brightness sensor.
4K HDMI, 100W PD, SD card, 3× USB-A.
Auto-focus, built-in ring light, noise-cancelling mic.
USB 3.2 Gen 2, 1050 MB/s read, shock-resistant.
Product reviews
See what other shoppers think — and leave your own.
Earbuds are great, fast delivery.
Keyboard feels premium for the price.
USB-C hub works perfectly with my MacBook.
🎯 Mission Control
SwiftShop was built fast and shipped with security as an afterthought. Twenty classes of weakness are hiding in this app. Find them, exploit them, then explain how a security-first design would stop each one.
⭐ Start here (easy wins)
17. Secrets in page source
Right-click → View Page Source (Ctrl+U), search "password".
Account → Forgot password? shows the real password on screen.
Click a product's price, change it, then add to cart.
Press Ctrl+A to reveal the white-on-white admin link in the footer.
Feed the system values it should never accept (negative qty, decimals).
Inject HTML/JS via reviews that runs for every visitor.
Craft a URL with a?promo= param that renders unsanitised HTML.
4. Broken Authentication
No rate limit, no lockout, plaintext passwords in the source.
Edit your session role in storage to reach the admin panel.
The profile update takes every field — including role and balance.
Hardcoded API keys, credentials, and card numbers in the source.
8. Direct Storage Tampering
Edit localStorage directly — change prices, balances, roles.
9. Insecure Deserialization
Import a cart from base64 JSON — the app trusts whatever you send.
Order IDs are sequential — view any order by changing the number.
11. Information Disclosure
Console.log leaks secrets; verbose errors expose internals.
12. Resource Misappropriation
Unlimited loyalty bonus, staff coupon in the code.
Refer yourself or reuse the same referral code endlessly.
Rapid-fire the bonus button — no mutex means multiple credits.
Change GLOBAL_DISCOUNT or cart functions from the console.
nukeStore() wipes everything — no auth, no confirmation needed.
💡 Tip: Open DevTools (F12) → Console / Application / Sources. The source code IS the vulnerability surface.